Information Security
- Policies and Basic Approach
- Structure (Governance)
- Training
- Systematic Technical Measures
- Supply Chain Security
- Security Support for DX
- Group Management of Information Security Risks
- Further Enhancement of the Information Security Framework
Promotion of Digital Transformation (DX)
- DX Promotion
- Structure and Human Resources
- DX Certification
- Enhancement of Management Information Infrastructure
Information Security
Policies and Basic Approach
The Inabata Group recognizes the importance of information security and, with the aim of protecting the Group’s information assets from information security risks, has established fundamental rules on information security in the form of an Information Security Policy. In addition, the Group has developed related regulations, including information management procedures, as well as manuals for all employees. These rules and manuals are reviewed on an ongoing basis to ensure a flexible response to new risks and technologies, while continuously improving information security management. Equivalent standards have also been implemented at domestic and overseas Group companies. In accordance with these rules, we will further strengthen information security measures across the entire Inabata Group and ensure compliance with laws, regulations, and contractual requirements related to information security.
We also strive to prevent the occurrence of information security incidents. In the unlikely event that an incident does occur, we will promptly implement appropriate measures, including not only incident response but also measures to prevent recurrence. With regard to personal information, the Group has established a Privacy Policy and a Policy on the Handling of Personal Information.
Structure (Governance)
Within the Group, recognizing the importance of information security and aiming to further promote company-wide initiatives, we have established an Information Security Working Committee as a subordinate body of the Compliance Committee, which is chaired by the president. The Information Security Working Committee is chaired by the general manager of the Digital Promotion Office, and its members include representatives from major sales divisions and administrative offices. In addition, a Secretariat for the Information Security Working Committee has been established within the Digital Promotion Office to handle committee operations and administrative matters related to information security. The Information Security Working Committee meets as necessary to deliberate on information security policies, rules, and detailed regulations, as well as to formulate education and training plans.
Moreover, an internal audit conducted by the information security auditor appointed by the chair of the Information Security Working Committee is carried out regularly once a year, and the results are reported to the chair.
The Compliance Committee, as the higher-level body, meets regularly four times a year and holds additional meetings as needed. At these meetings, the Chair of the Information Security Working Committee reports on important matters deliberated and addressed by the Working Committee, as well as on the results of internal audits. Significant matters discussed by the Compliance Committee are reported, as necessary, to the Management Council and the Board of Directors, and are subject to oversight by the Board. In addition, the status of information security initiatives is reported to the Board of Directors on a quarterly basis through business execution reports, thereby ensuring effective Board oversight.
With regard to execution functions (planning, promotion, and implementation), we have established a Security Incident Response Team (IK-SIRT*) to enable swift and accurate responses to increasingly sophisticated security incidents. We have also appointed information security administrators in sales divisions and administrative offices, as well as information security officers in major domestic and overseas subsidiaries. These personnel oversee information security within their respective organizations, compile the status of compliance with information security policies, rules, and detailed regulations, and report regularly to the Information Security Working Committee through the Secretariat.
We also cooperate, as necessary, with various external organizations to further strengthen our information security structure.
- *IK-SIRT: A term combining the Group’s symbol “IK” and an acronym for “Security Incident Response Team.”

Training
The Information Security Working Committee provides regular information security awareness training for all officers and employees of the Company, including fixed-term contract employees, temporary agency workers, employees seconded to other companies, and employees seconded from other companies.
In addition to incorporating information security awareness training into annual new employee training, information security awareness training is conducted at joint training sessions held annually from August to September. The theme for 2025 was “Cyberattacks Already Among Us” and the training was conducted in multiple languages, including Japanese, English, and Chinese.
Systematic Technical Measures
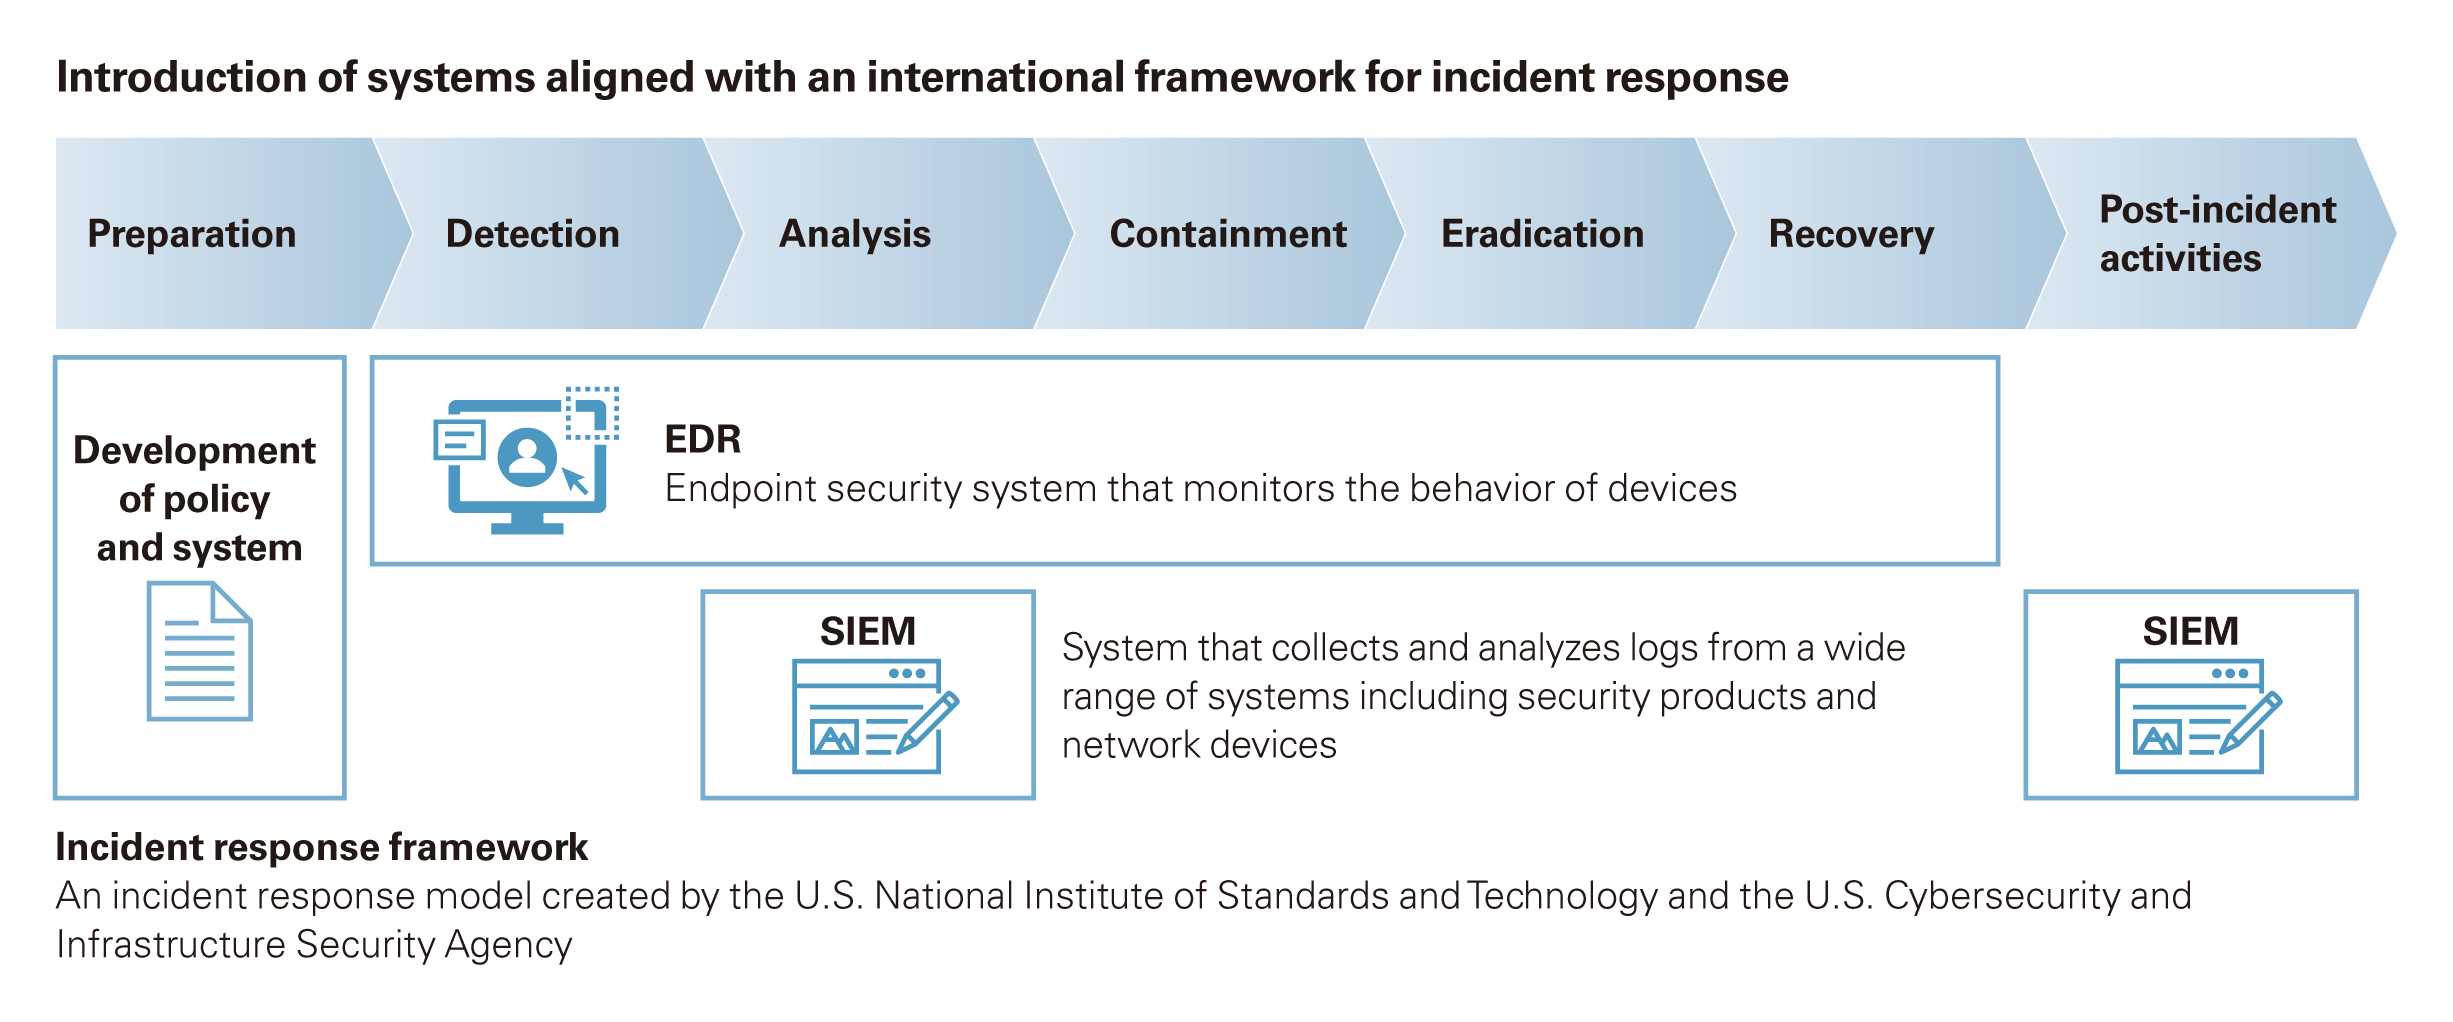
As systematic technical measures against security incidents, we have implemented and operate systems in line with international frameworks for incident response. To detect, analyze, contain, and eradicate cyberattacks, we deploy endpoint security systems that monitor endpoint behavior and enable remote containment and eradication of threats. In addition, we utilize a security information and event management (SIEM) system that aggregates logs from all systems (including security products and network devices) to conduct post-incident responses such as cause analysis and formulation of measures to prevent recurrence.
Supply Chain Security
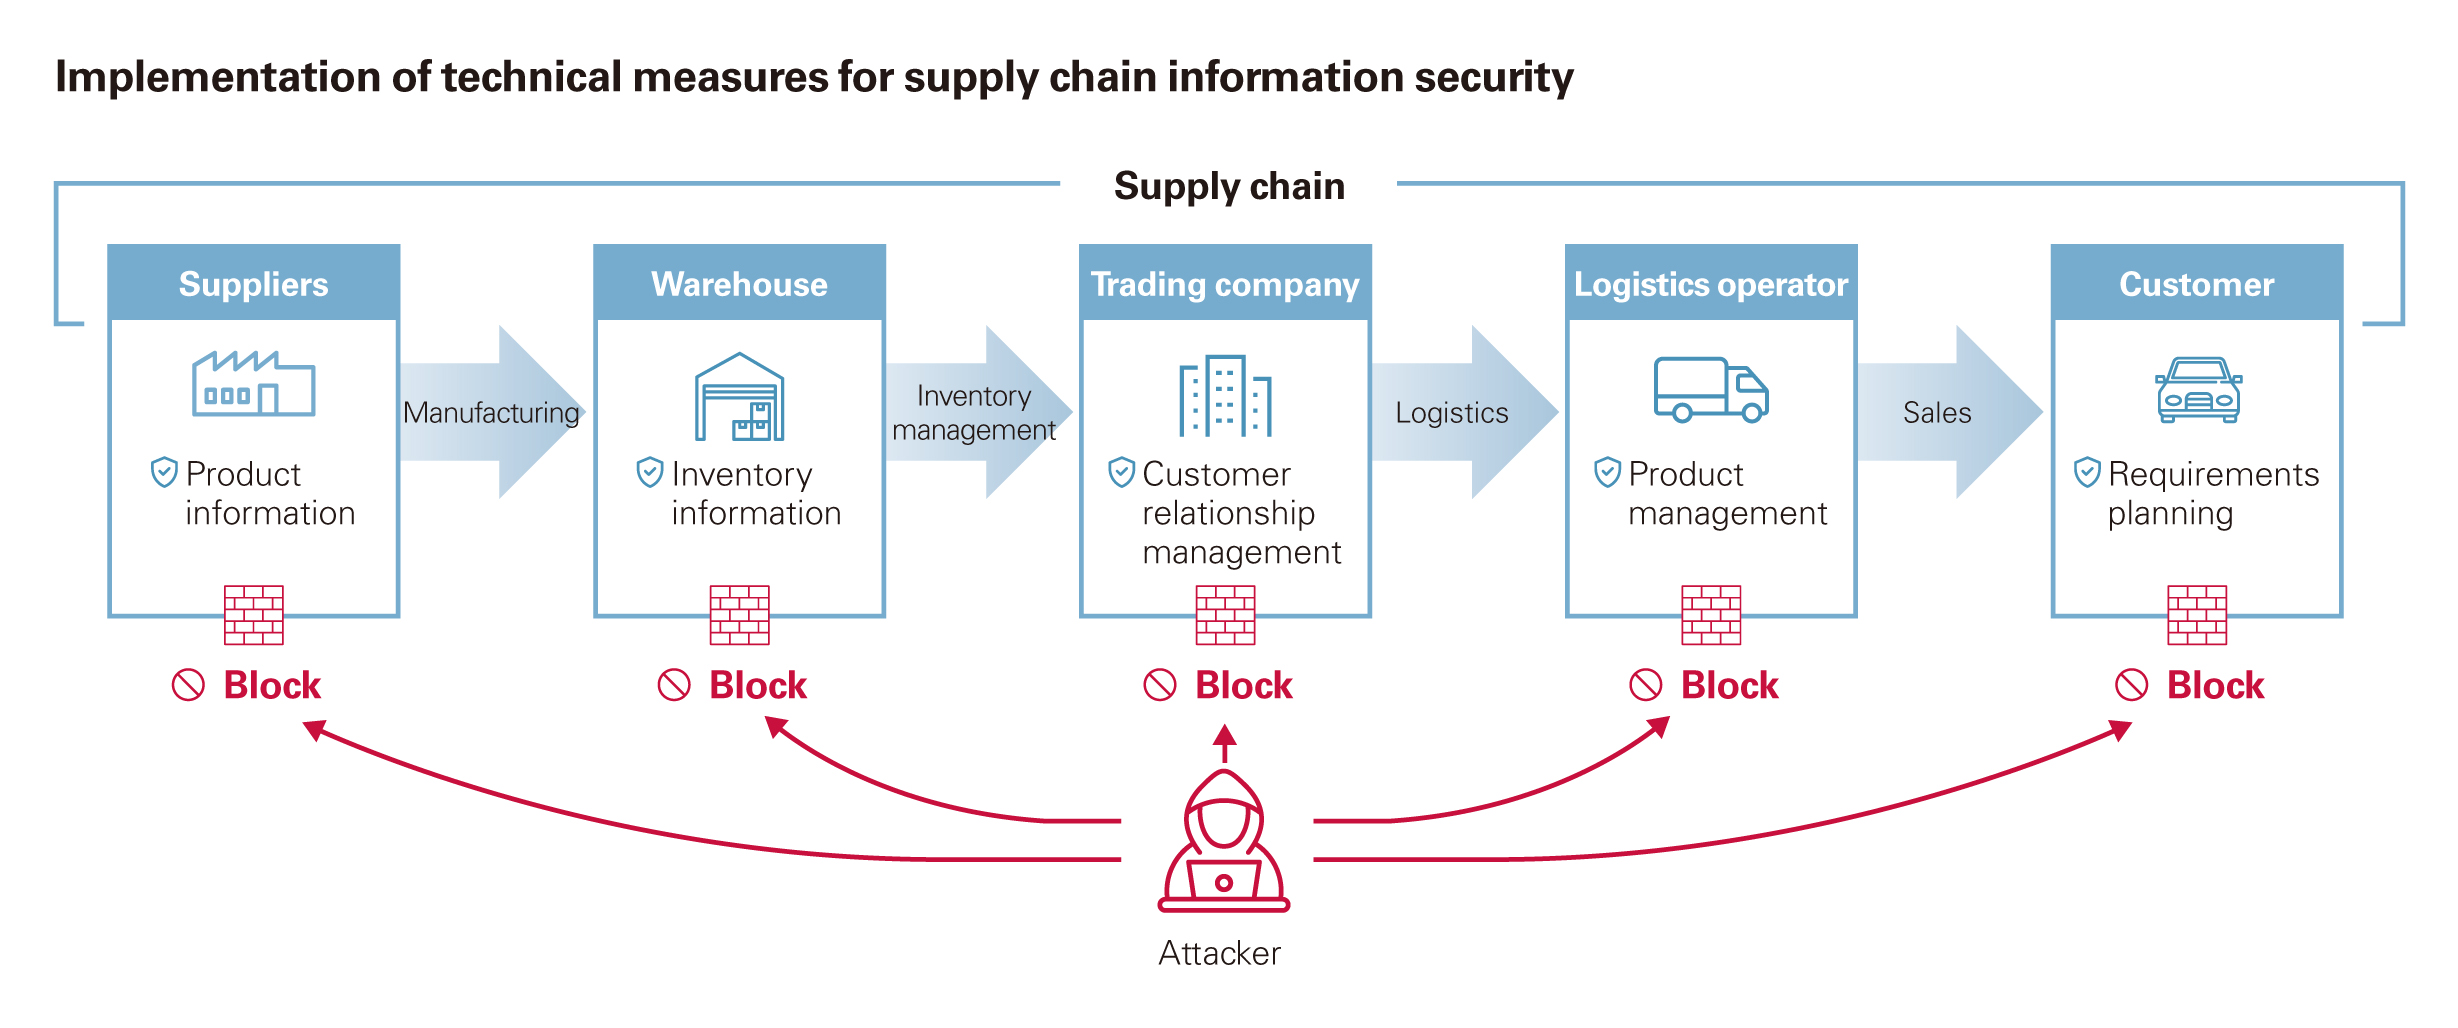
With respect to information security across the entire supply chain comprising suppliers and customers, the Group fulfills its accountability through questionnaires and surveys administered from individual business partners.
Furthermore, in order to contribute to increased security of the entire supply chain, we continuously enhance management systems and technical measures for confidential information against vulnerabilities in information systems.
Security Support for DX
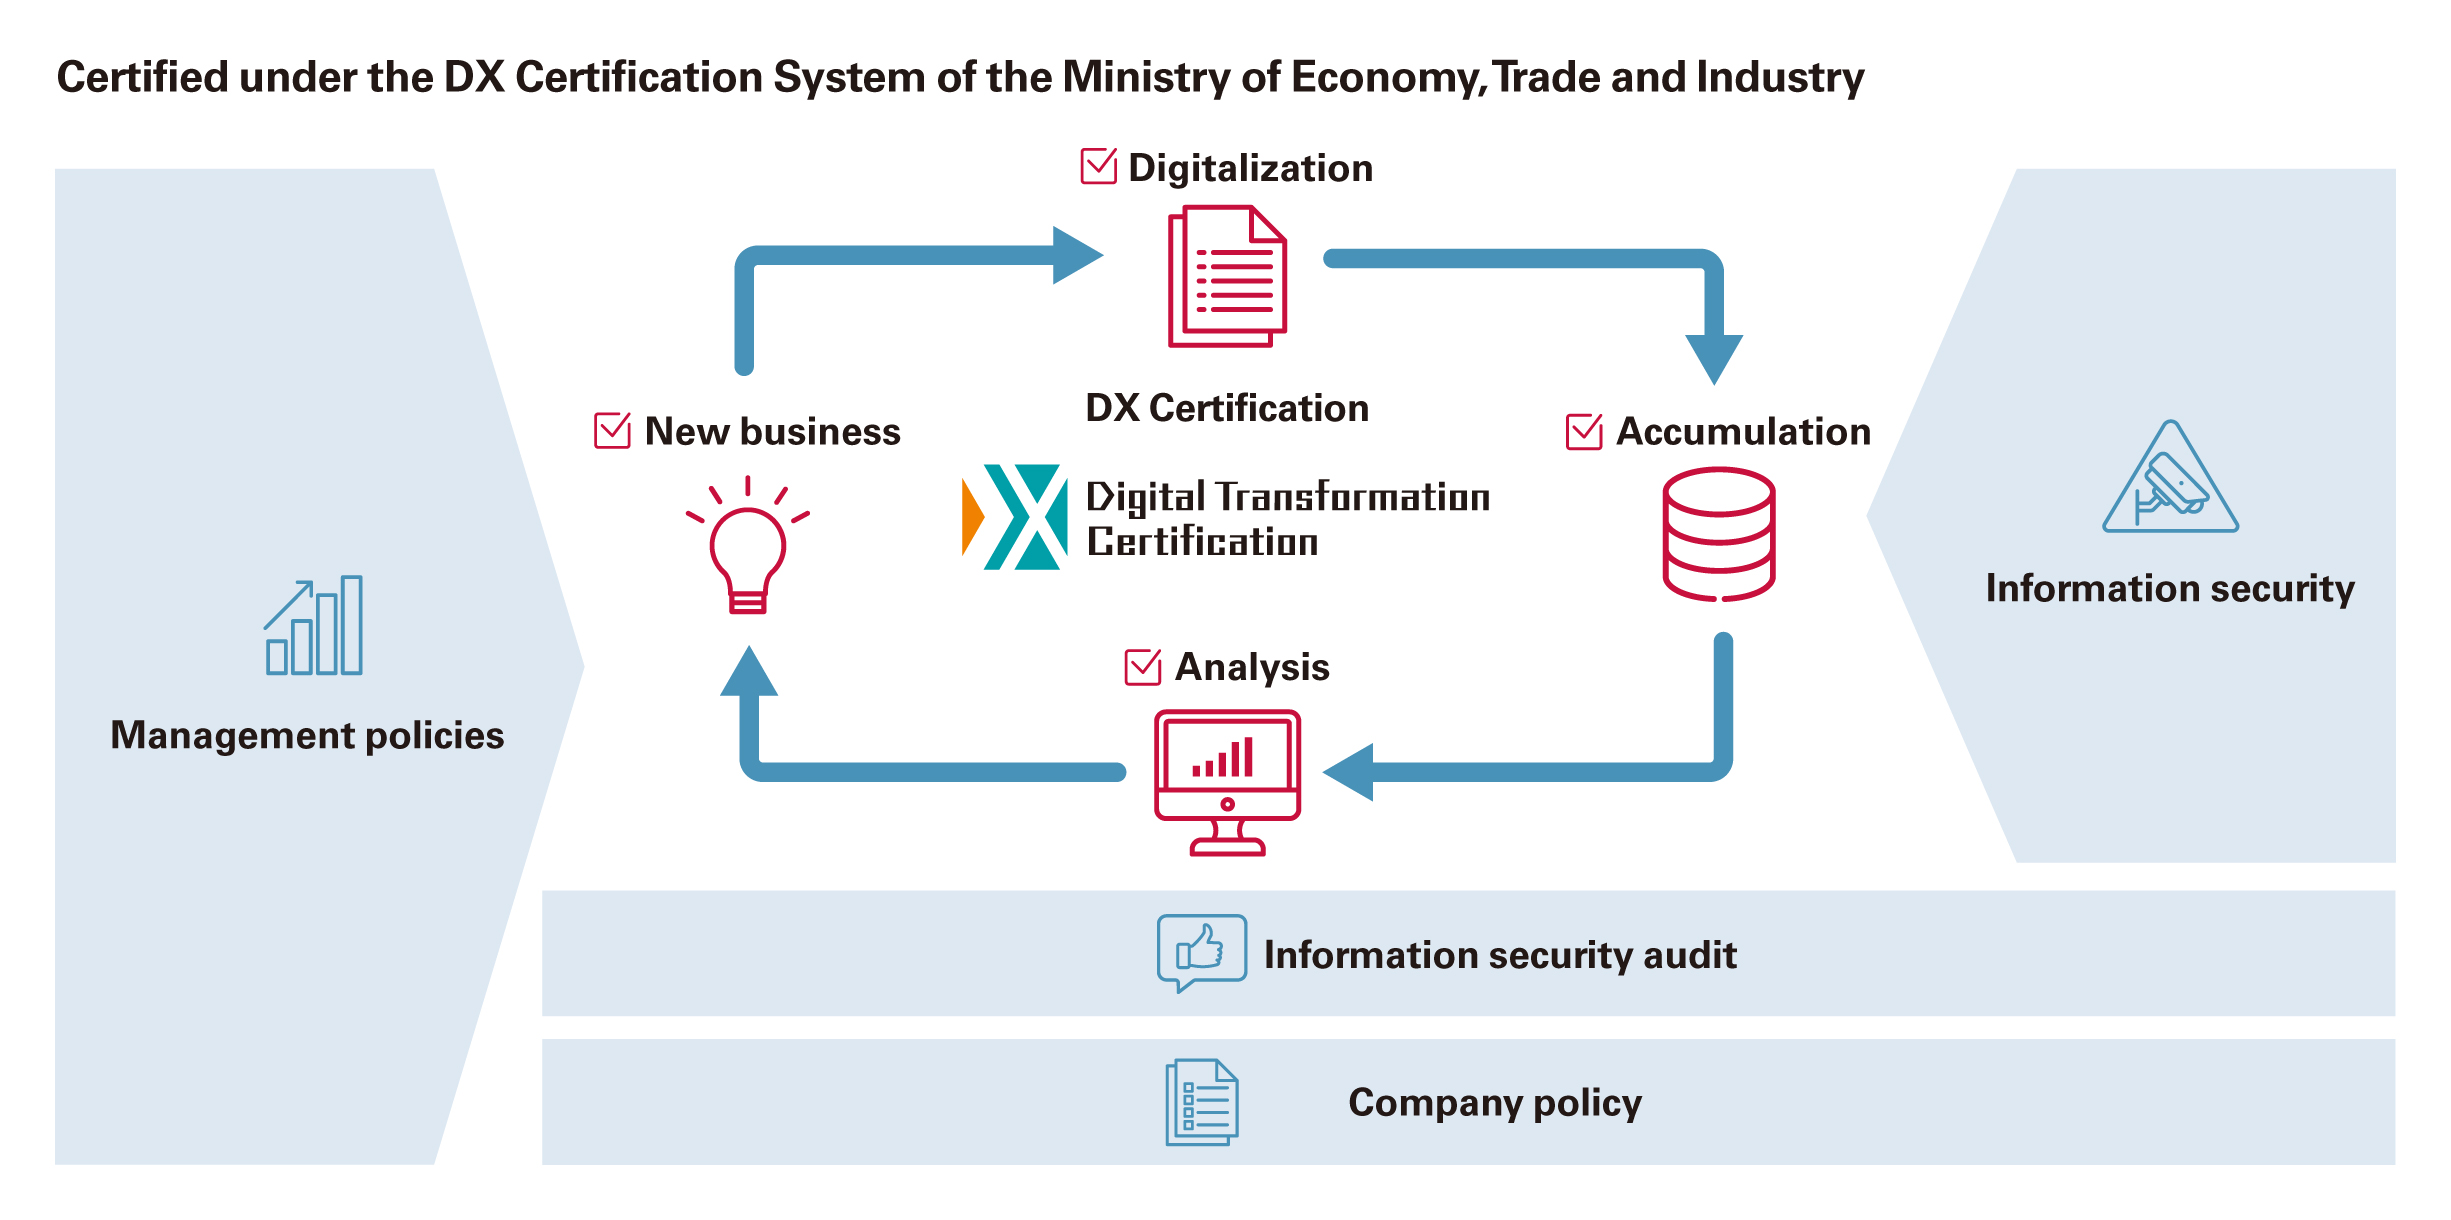
On March 1, 2023, we were certified as a DX business operator under the DX Certification System established by the Ministry of Economy, Trade and Industry of Japan. (see “DX Promotion” below).
In promoting DX strategies in line with management policies, we conduct regular information security audits to address information security risks, thereby confirming thorough communication of and compliance with internal rules. Also, we strive to develop and secure specialized security personnel in order to achieve management strategy objectives and ensure information security.
Group Management of Information Security Risks
Information security measures are a critical priority for the entire Group. We have implemented information security policies for both domestic and overseas Group companies that are on par with those of Inabata & Co., Ltd. However, there are discrepancies in the level of information security among consolidated subsidiaries, and the risk levels vary from company to company. To address this issue, the Information Security Working Committee has formulated Information Security Guidelines for consolidated subsidiaries. These initiatives aim to enhance the foundations of security governance across the entire Group.
In addition to implementing various risk management measures, including those mentioned above, we have also taken steps to manage the risk of unforeseen security incidents that may still occur. As part of this risk management strategy, we enrolled all consolidated subsidiaries in cyber insurance starting in April 2024.
Risk Reduction
Formulation of Information Security Guidelines
Clearly outline the information security initiatives that should be implemented by the end of FY2024, promote measures across each Group company, and reduce risks to an acceptable level.
Risk Transfer
Enrollment in Cyber Insurance
Target: All consolidated subsidiaries
Coverage: Compensation for damages, investigation and recovery costs, etc.
Further Enhancement of the Information Security Framework
Cybersecurity Incident Drills from a Business Continuity Perspective
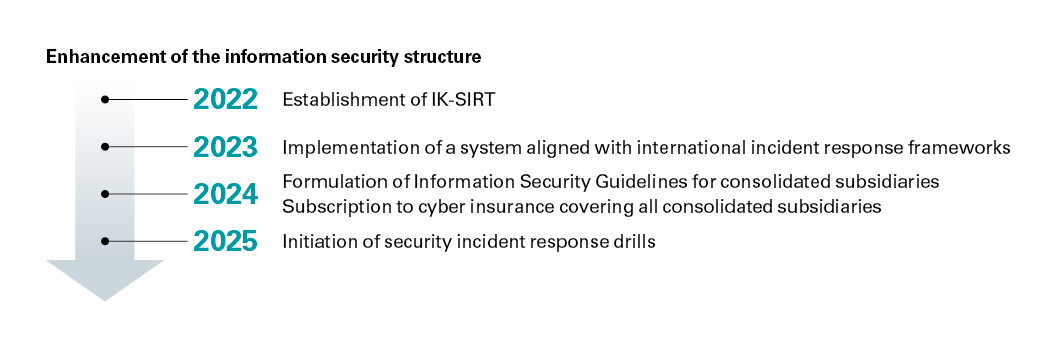
Three years have passed since the establishment of IK-SIRT in 2022, during which the Inabata Group has steadily accumulated knowledge and experience in incident response. In 2025, with the goal of further enhancing the information security structure and ensuring business continuity, we conducted drills simulating cybersecurity incidents across the Group. These exercises focused on establishing a communication system for rapid coordination with internal and external organizations, updating manuals, and reviewing response workflows. Regular practical drills for security incident response are planned.
DX Promotion
We set "digital strategy" as one of the management foundation strategies in the medium-term management plan New Challenge 2026 (NC2026) which started in FY2024. The enhancement of information security and the promotion of DX are two essential parts of our efforts.
DX Strategy Policy
Further enhancement of global management information infrastructure
- We will strive to adapt to new technological trends, achieve further digitalization, and transform and streamline operations (DX initiatives)
- We will establish a global management information infrastructure that supports the enhancement of security, business continuity planning, and new ways of working

Structure and Human Resources
Renewal of the Information Systems Department: Promotion of Securing and Developing Digital Talent
In April 2022, in order to further promote DX, we selected business leaders from each sales division for a company-wide project. We are developing human resources capable of analyzing management information. Furthermore, we have renewed the existing information systems department into an organization focused on DX.

DX Certification
On March 1, 2025, we renewed our certification as a DX business operator under the DX (Digital Transformation) Certification System* established by the Ministry of Economy, Trade and Industry. We were initially certified in 2023. As a result of this review, our certification has been approved through the end of FY2027.

Note: The DX Certification System is a certification program established by the Ministry of Economy, Trade and Industry to encourage companies’ voluntary efforts in digital transformation (DX). It certifies companies that are recognized as “DX-Ready,” meaning they are prepared to transform their business through digital means, based on the Act on Facilitation of Information Processing.
DX Certification System on the Ministry of Economy, Trade and Industry website (Japanese only)
Enhancement of Management Information Infrastructure
In 2022, the Information Technology Office was renamed the Digital Promotion Office to further advance digitalization and enhance feedback to our businesses.
Data-Driven Management Leveraging Management Base Data
As part of the digital strategy under the medium-term management plan NC2026 that started in FY2024, we are advancing initiatives to promote data-driven management that leverages management base data.
The Inabata Group operates globally and handles a wide range of products. To become a data-driven company making decisions based on a Group-wide data platform, we have integrated master data for companies and products and systematized the automatic aggregation of consolidated results. This has led to the establishment of the global Consolidated Performance Data Management (CDAM*) system, which provides visibility into the business flow.
Previously, collecting consolidated figures for monthly closing involved a significant amount of manual work. With this system, approximately 90% of management information across the Group, including both the parent company and consolidated subsidiaries, can now be viewed instantly in a centralized manner, improving operational efficiency and supporting faster management decision-making.
- *CDAM: Consolidated Performance Data Management
Improve Productivity by Leveraging Generative AI Services
As part of the digital strategy under NC2026, we are promoting company-wide initiatives to improve productivity by leveraging generative AI services.
Since FY2023, we have conducted a trial of Microsoft Copilot, with 210 participants from all departments testing its application for operational efficiency. Among participants, 45% reported improvements in work speed and quality, and for certain tasks, 28% confirmed anticipated cost-effectiveness.
From FY2024, we have also begun using a closed generative AI environment, Azure OpenAI, within the Company to analyze internal sales information. By leveraging generative AI to extract customer insights from unstructured data in the sales division, such as daily work reports, we aim to enhance marketing activities.
We will continue to advance initiatives to further improve operational efficiency in line with the evolving capabilities of AI technologies.